
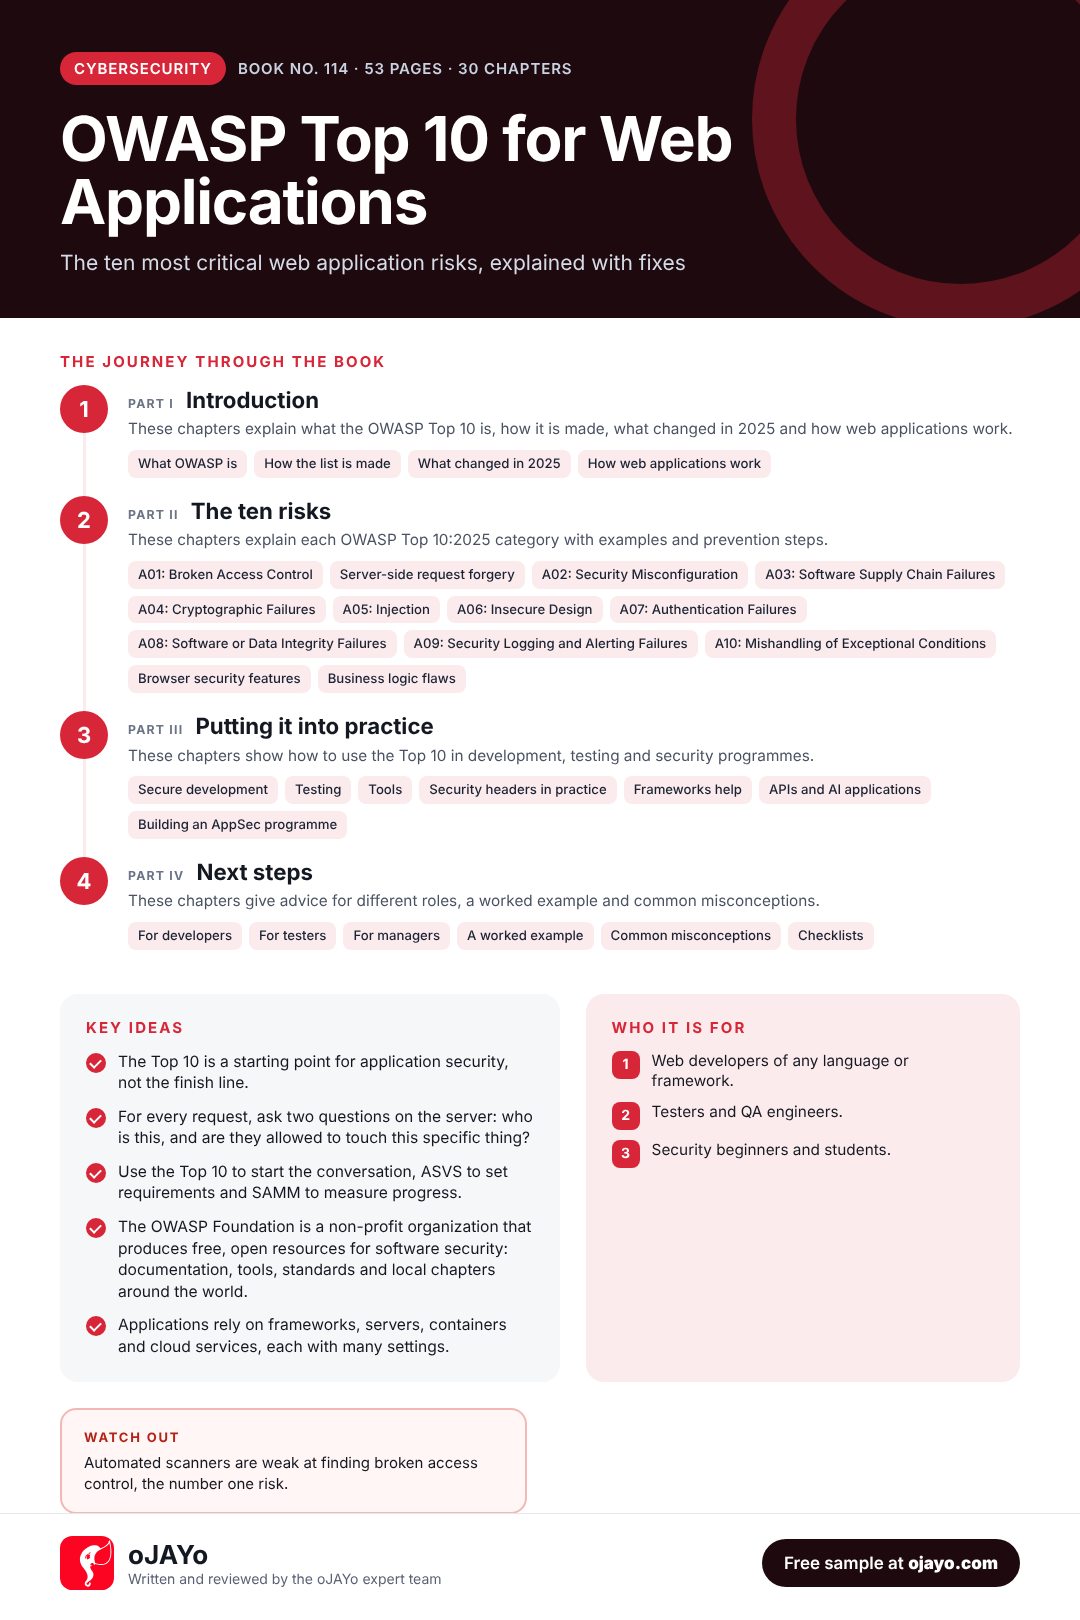
OWASP Top 10 for Web Applications: The ten most critical web application risks, explained with fixes. It is a 53-page illustrated PDF from the oJAYo team, written in plain language and up to date for 2026.
The OWASP Top 10 is the best-known list of the most critical security risks to web applications. Published by the Open Worldwide Application Security Project (OWASP), a non-profit community, it is used by developers, testers, auditors and regulators around the world as a common language for application security.
The latest edition, the OWASP Top 10:2025, was presented in November 2025 and finalized in January 2026. It is the first major update since 2021 and adds two new categories: software supply chain failures and mishandling of exceptional conditions.
Why buy OWASP Top 10 for Web Applications?
- Created by the oJAYo team of security experts: written by practitioners, then technically reviewed and edited.
- Turns a big security topic into clear, practical steps you can use at work right away.
- 31 short, focused chapters you can read in one sitting each, so steady progress fits around a busy week.
- Plain-language explanations with diagrams, so you understand the why as well as the how.
- Up to date for 2026, covering today’s threats, tools and frameworks.
- Defensive and practical: checklists and real-world examples instead of jargon.
- Ready-to-use checklists you can take straight into your next project or review.
- Instant PDF download that works on any laptop, tablet or phone, yours to keep.
What you will learn
- What OWASP is
- How the list is made
- What changed in 2025
- How web applications work
- Reading the categories
- A01: Broken Access Control
- Server-side request forgery
- A02: Security Misconfiguration
- A03: Software Supply Chain Failures
- A04: Cryptographic Failures
- A05: Injection
- A06: Insecure Design
- A07: Authentication Failures
- A08: Software or Data Integrity Failures
Who this book is for
- Web developers of any language or framework.
- Testers and QA engineers.
- Security beginners and students.
- Managers responsible for application security.
What is inside
- Format: PDF, instant download
- Length: 53 pages
- Chapters: 31
- Diagrams and screens: 17
- Created by: the oJAYo expert team (written, technically reviewed and edited)
- Publisher: oJAYo.com
- Published: 2026
- Series number: No. 114
Frequently asked questions
What does OWASP Top 10 for Web Applications cover?
Topics include “How the list is made”, “How web applications work”, “Reading the categories”, “A01: Broken Access Control” and “Server-side request forgery”, across 31 chapters with 17 diagrams and illustrated screens.
Who should read OWASP Top 10 for Web Applications?
Web developers of any language or framework. Testers and QA engineers. Security beginners and students.
Is it suitable for beginners?
Yes. It starts from the basics and builds up step by step, with a glossary for any term that is new to you.
What format is the book, and how do I get it?
It is a 53-page PDF. After checkout you get an instant download link, and you can read it on any device.
Is the content up to date?
Yes. It was written, reviewed and published in 2026 by the oJAYo team at oJAYo.com and reflects current versions, tools and practices.
OWASP is a registered trademark of the OWASP Foundation. This book is not affiliated with or endorsed by the OWASP Foundation.
Get OWASP Top 10 for Web Applications for $49 and start reading in minutes.



Reviews
There are no reviews yet.