
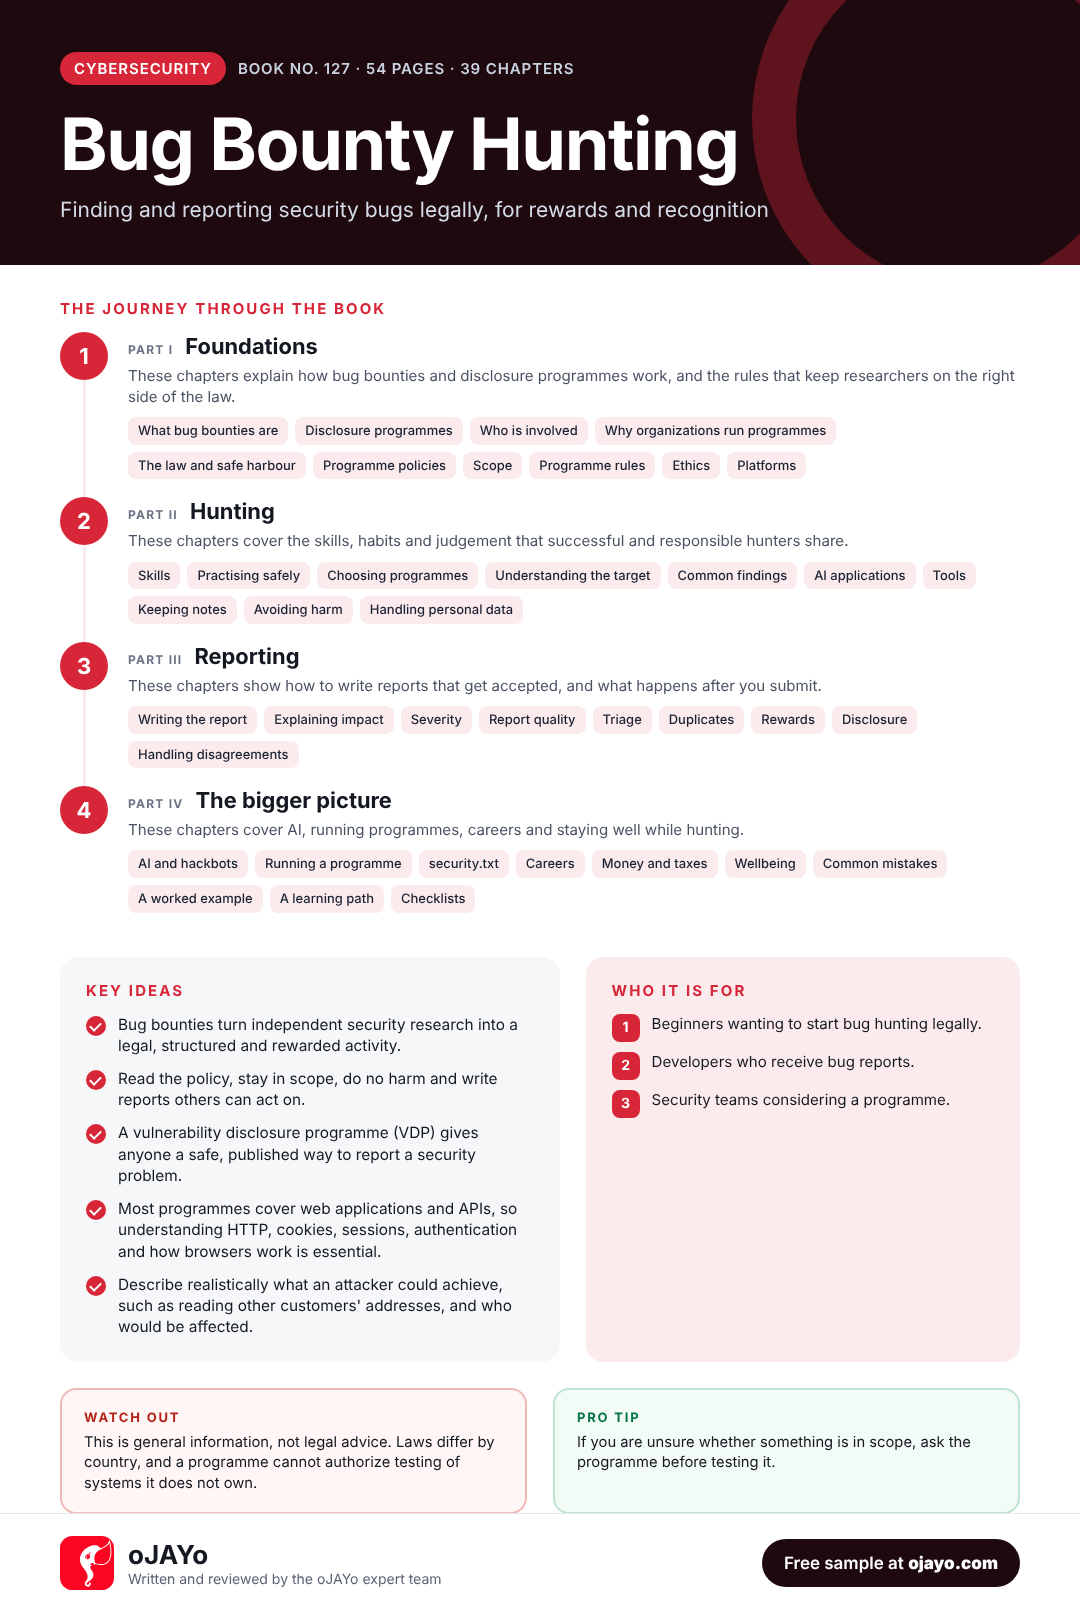
Bug Bounty Hunting: Finding and reporting security bugs legally, for rewards and recognition. It is a 54-page illustrated PDF from the oJAYo team, written in plain language and up to date for 2026.
A bug bounty programme invites independent security researchers to find and report vulnerabilities in an organization’s systems, and rewards valid reports, usually with money. Thousands of organizations, from tech giants to governments, run such programmes, and many researchers learn their craft through them.
This beginner’s book explains how bug bounties and vulnerability disclosure work, how to read a programme policy, the rules and ethics that keep you legal, how to practise, how to write a report that gets accepted, and how organizations can run their own programmes. It focuses on process and judgement rather than attack techniques.
Why buy Bug Bounty Hunting?
- Created by the oJAYo team of security experts: written by practitioners, then technically reviewed and edited.
- Turns a big security topic into clear, practical steps you can use at work right away.
- 38 short, focused chapters you can read in one sitting each, so steady progress fits around a busy week.
- Plain-language explanations with diagrams, so you understand the why as well as the how.
- Up to date for 2026, covering today’s threats, tools and frameworks.
- Defensive and practical: checklists and real-world examples instead of jargon.
- Ready-to-use checklists you can take straight into your next project or review.
- Instant PDF download that works on any laptop, tablet or phone, yours to keep.
What you will learn
- What bug bounties are
- Disclosure programmes
- Who is involved
- Why organizations run programmes
- The law and safe harbour
- Programme policies
- Scope
- Programme rules
- Ethics
- Platforms
- Skills
- Practising safely
- Choosing programmes
- Understanding the target
Who this book is for
- Beginners wanting to start bug hunting legally.
- Developers who receive bug reports.
- Security teams considering a programme.
What is inside
- Format: PDF, instant download
- Length: 54 pages
- Chapters: 38
- Diagrams and screens: 13
- Created by: the oJAYo expert team (written, technically reviewed and edited)
- Publisher: oJAYo.com
- Published: 2026
- Series number: No. 127
Frequently asked questions
What does Bug Bounty Hunting cover?
Topics include “Disclosure programmes”, “Who is involved”, “Why organizations run programmes”, “The law and safe harbour” and “Programme policies”, across 38 chapters with 13 diagrams and illustrated screens.
Who should read Bug Bounty Hunting?
Beginners wanting to start bug hunting legally. Developers who receive bug reports. Security teams considering a programme.
Is it suitable for beginners?
Yes. It starts from the basics and builds up step by step, with a glossary for any term that is new to you.
What format is the book, and how do I get it?
It is a 54-page PDF. After checkout you get an instant download link, and you can read it on any device.
Is the content up to date?
Yes. It was written, reviewed and published in 2026 by the oJAYo team at oJAYo.com and reflects current versions, tools and practices.
Platform, product and company names mentioned in this book are trademarks of their respective owners.
Get Bug Bounty Hunting for $49 and start reading in minutes.


Reviews
There are no reviews yet.